Search

Saved articles

You have not yet added any article to your bookmarks!

Browse articles

GDPR Compliance

We use cookies to ensure you get the best experience on our website. By continuing to use our site, you accept our use of cookies, Privacy Policy, and Terms of Service.

Fake job interviews, AI tool breach enabled $6.34-billion cyberattack: Binance

Fake job interviews, AI tool breach enabled $6.34-billion cyberattack: Binance

The exchange said the malware used “sophisticated obfuscation and evasion techniques” to avoid detection and establish communication with an attacker-controlled external server.

பகிரவும் WhatsApp Facebook

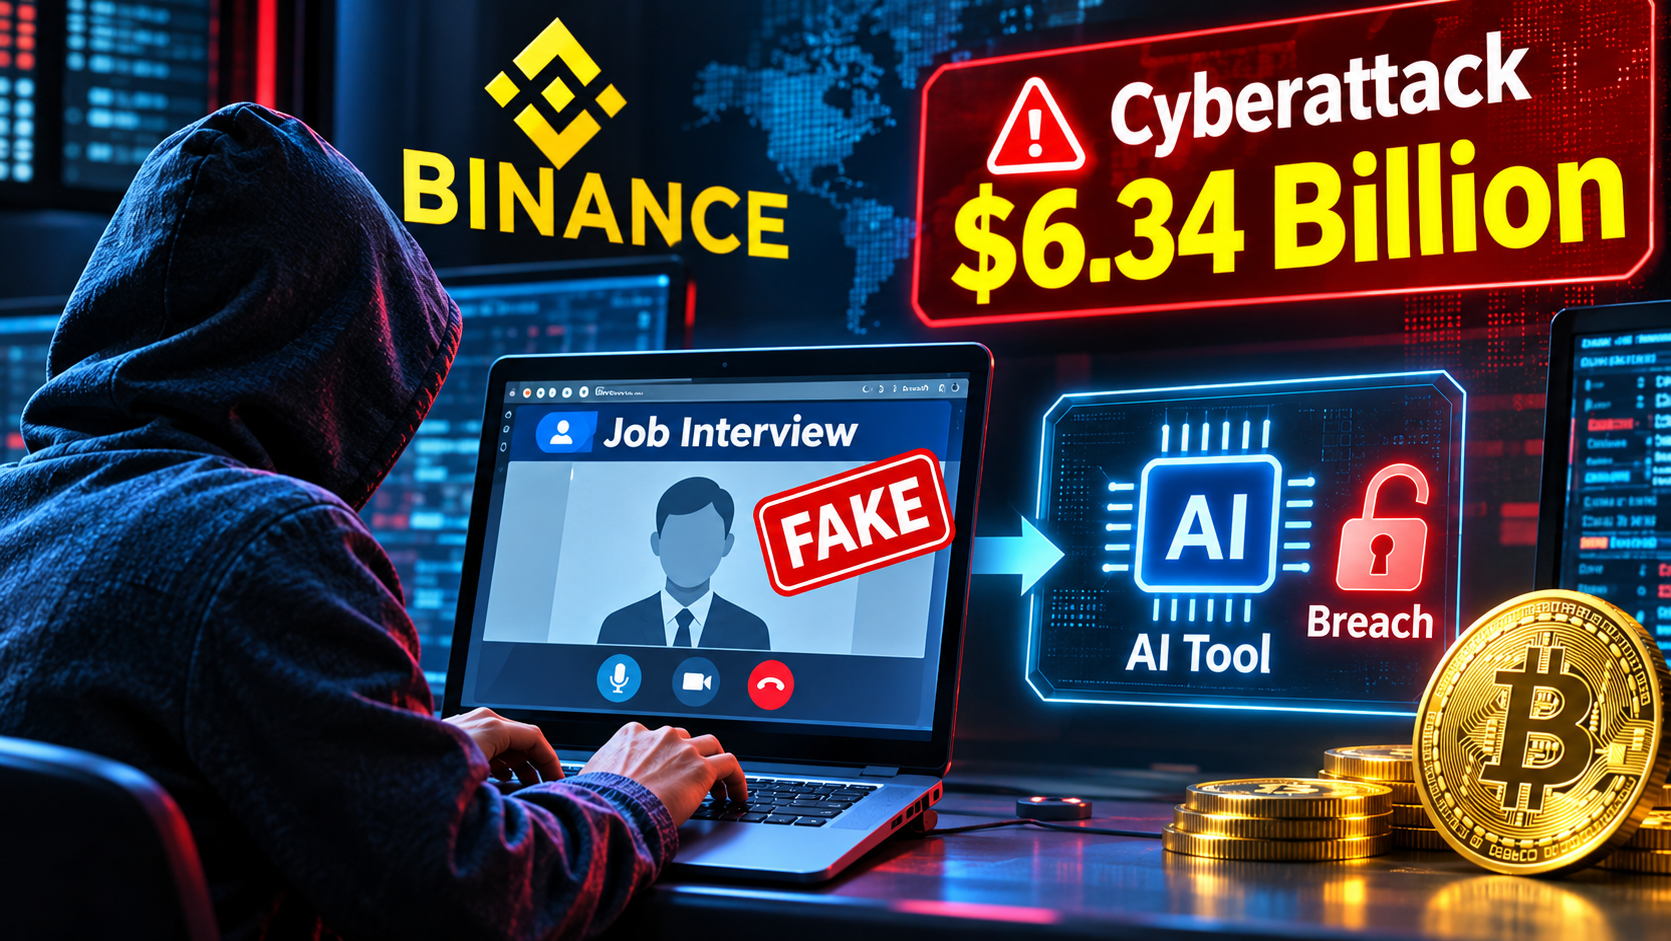
Cryptocurrency exchange Binance has revealed that attackers used fake recruitment interviews, malicious software and a compromised internal artificial intelligence (AI) tool to gain access to its systems before stealing around $6.34 billion in digital assets in an October 29 security breach.

In its latest incident update on X, Binance described the attack as a “sophisticated, multi-stage campaign” and said it was “not a single isolated breach or a simple phishing incident”. The exchange said the attackers combined social engineering, malicious software downloads, compromised internal AI tooling and an advanced transaction-authorisation method.

According to Binance's investigation, an engineer was approached in September by an individual posing as a project director through a job-hunting platform. After two rounds of interviews, the employee was instructed to download a malicious code repository disguised as an assignment onto his work computer.

The exchange said the malware used “sophisticated obfuscation and evasion techniques” to avoid detection and establish communication with an attacker-controlled external server.

On October 20, the attackers used the compromised computer and an internal AI tool to gain access to other employees and obtain credentials and permissions linked to wallet infrastructure, according to Binance.

On October 29, the attackers used the compromised access to reach Binance's internal wallet signing service. “The attacker exploited unauthorized access to an internal wallet signing service to initiate transactions outside the normal withdrawal process,” the company said.

Binance said approximately $6.34 billion in digital assets were impacted, of which around $2.85 billion had been frozen or intercepted as of its latest update, subject to reconciliation and market price movements.

The exchange said it had set aside more than 100% of the funds required to cover the losses. As of October 31, 98% of the affected token assets had been replenished, with the company purchasing the remaining, less liquid assets.

“Our first responsibility is to protect users. Binance will absorb the financial impact of the stolen funds, not our users,” the company said.

Binance has rebuilt the affected wallet system and internal AI tool, replaced compromised devices, revoked credentials and strengthened wallet-service controls. It is also engaging independent cybersecurity firms for an assessment and said it was increasing investment in “AI-enabled detection, endpoint protection, developer-environment security and behavioural anomaly monitoring”.

The Federal Bureau of Investigation (FBI) had attributed the attack to North Korea on Sunday, identifying it as the ‘TraderTraitor’ operation, a label used by US authorities for North Korean-linked cyber operations targeting cryptocurrency platforms.

The agency had also urged exchanges and other virtual asset service providers to block transactions linked to the stolen funds.

Binance said its investigation remains ongoing and that its findings would be subject to further independent review. - ANI

முந்தைய செய்தி
தென்கொரியாவில் இறக்குமதி கார் விற்பனை 29.3% உயர்வு
அடுத்த செய்தி
ஜெலென்ஸ்கியின் முன்னாள் செய்தித் தொடர்பாளர் யூலியா மீது தேச துரோக குற்றச்சாட்டு

தொடர்புடைய செய்திகள்